November's Secure AI & Governance Briefing: agent connector controls, agent accounts, a Mythos-ready playbook and the hero links deadline.
AI risk rarely arrives as a breach. It arrives as a default: a connector anyone can add, an account nobody reviewed, a sharing link your policies don't cover. This month, we look at the settings that quietly decide how exposed your AI really is. The question is no longer, "Did we turn the right controls on?" It is now:
AI that reasons like a pen tester can turn weeks of reconnaissance into hours. It doesn't need an exploit. It needs a "temporary" Conditional Access exclusion, an app still holding permissions from a finished project, or an agent whose maker has left. Exposure lives in the defaults you stopped looking at. Kanwal Khipple's free playbook covers 12 misconfigurations attackers' chain together, a 15-minute scorecard and a 90-day plan using controls you already license.
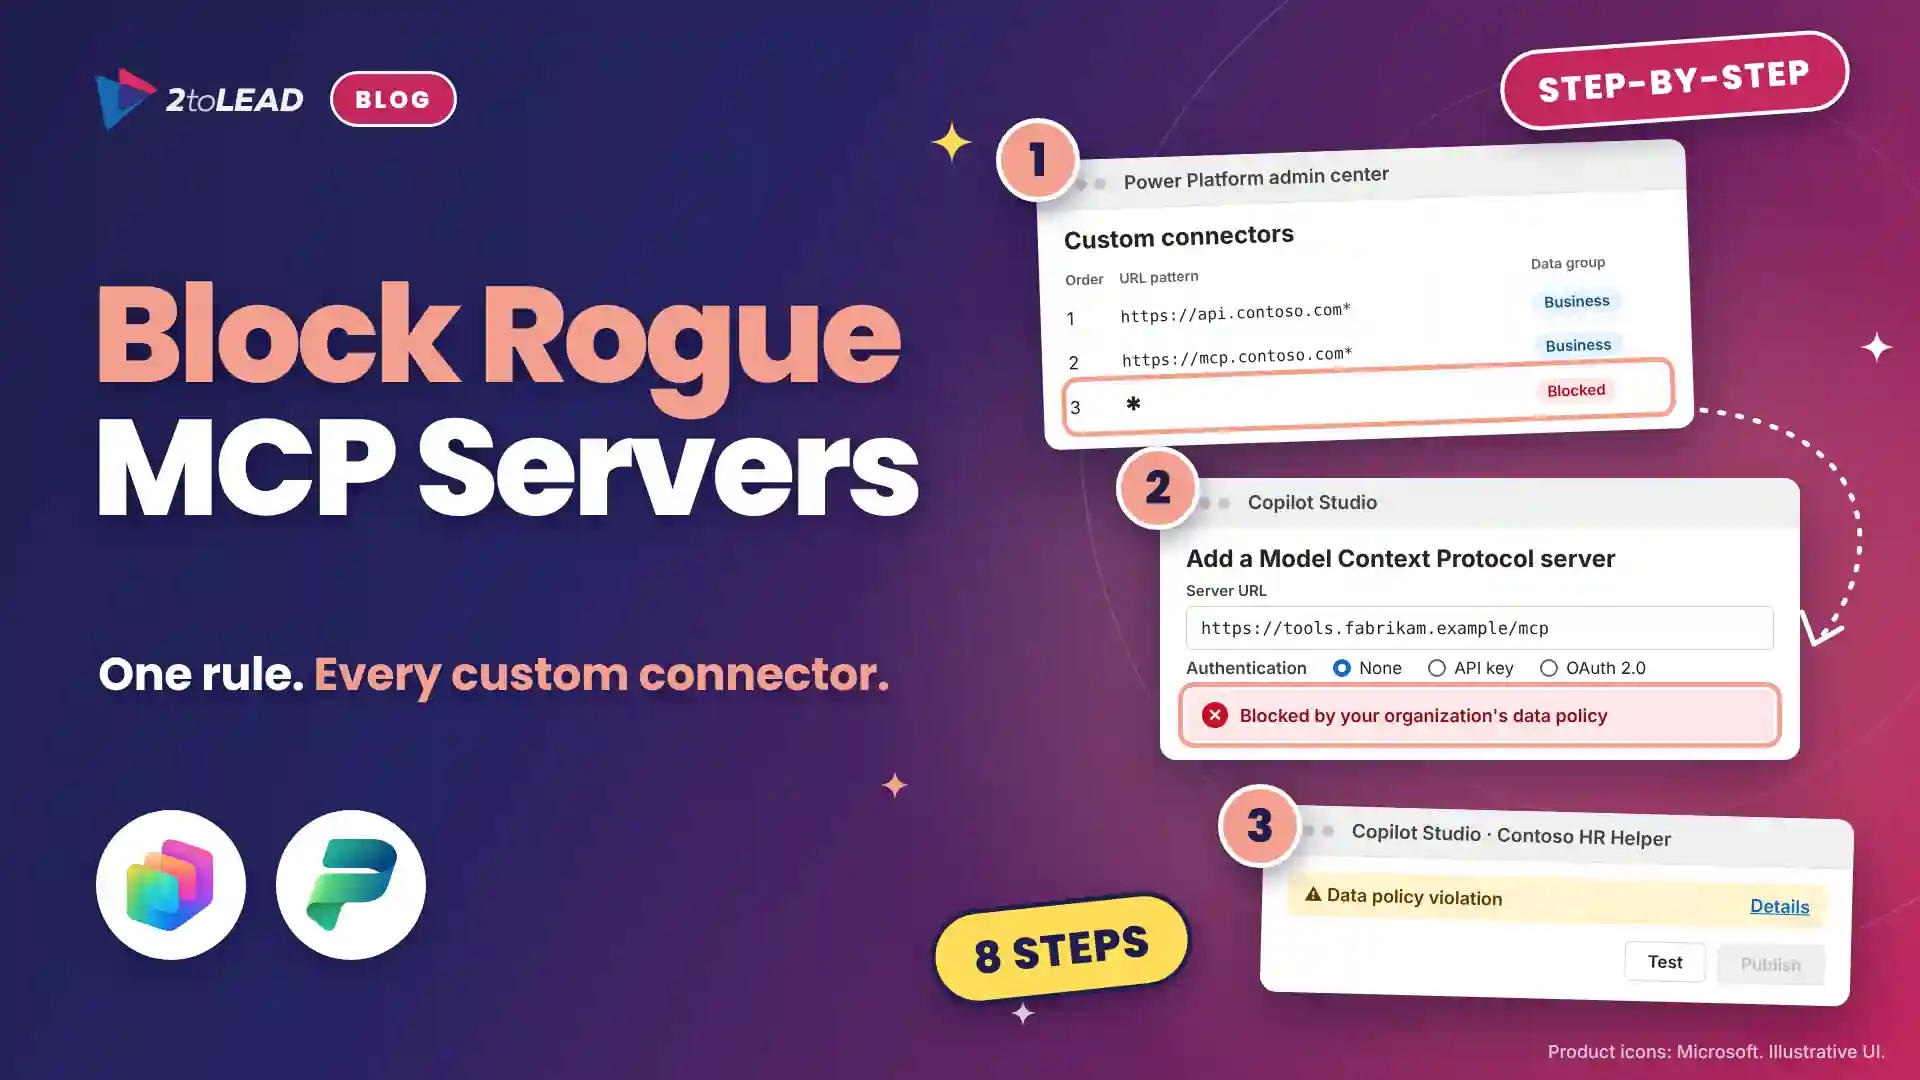
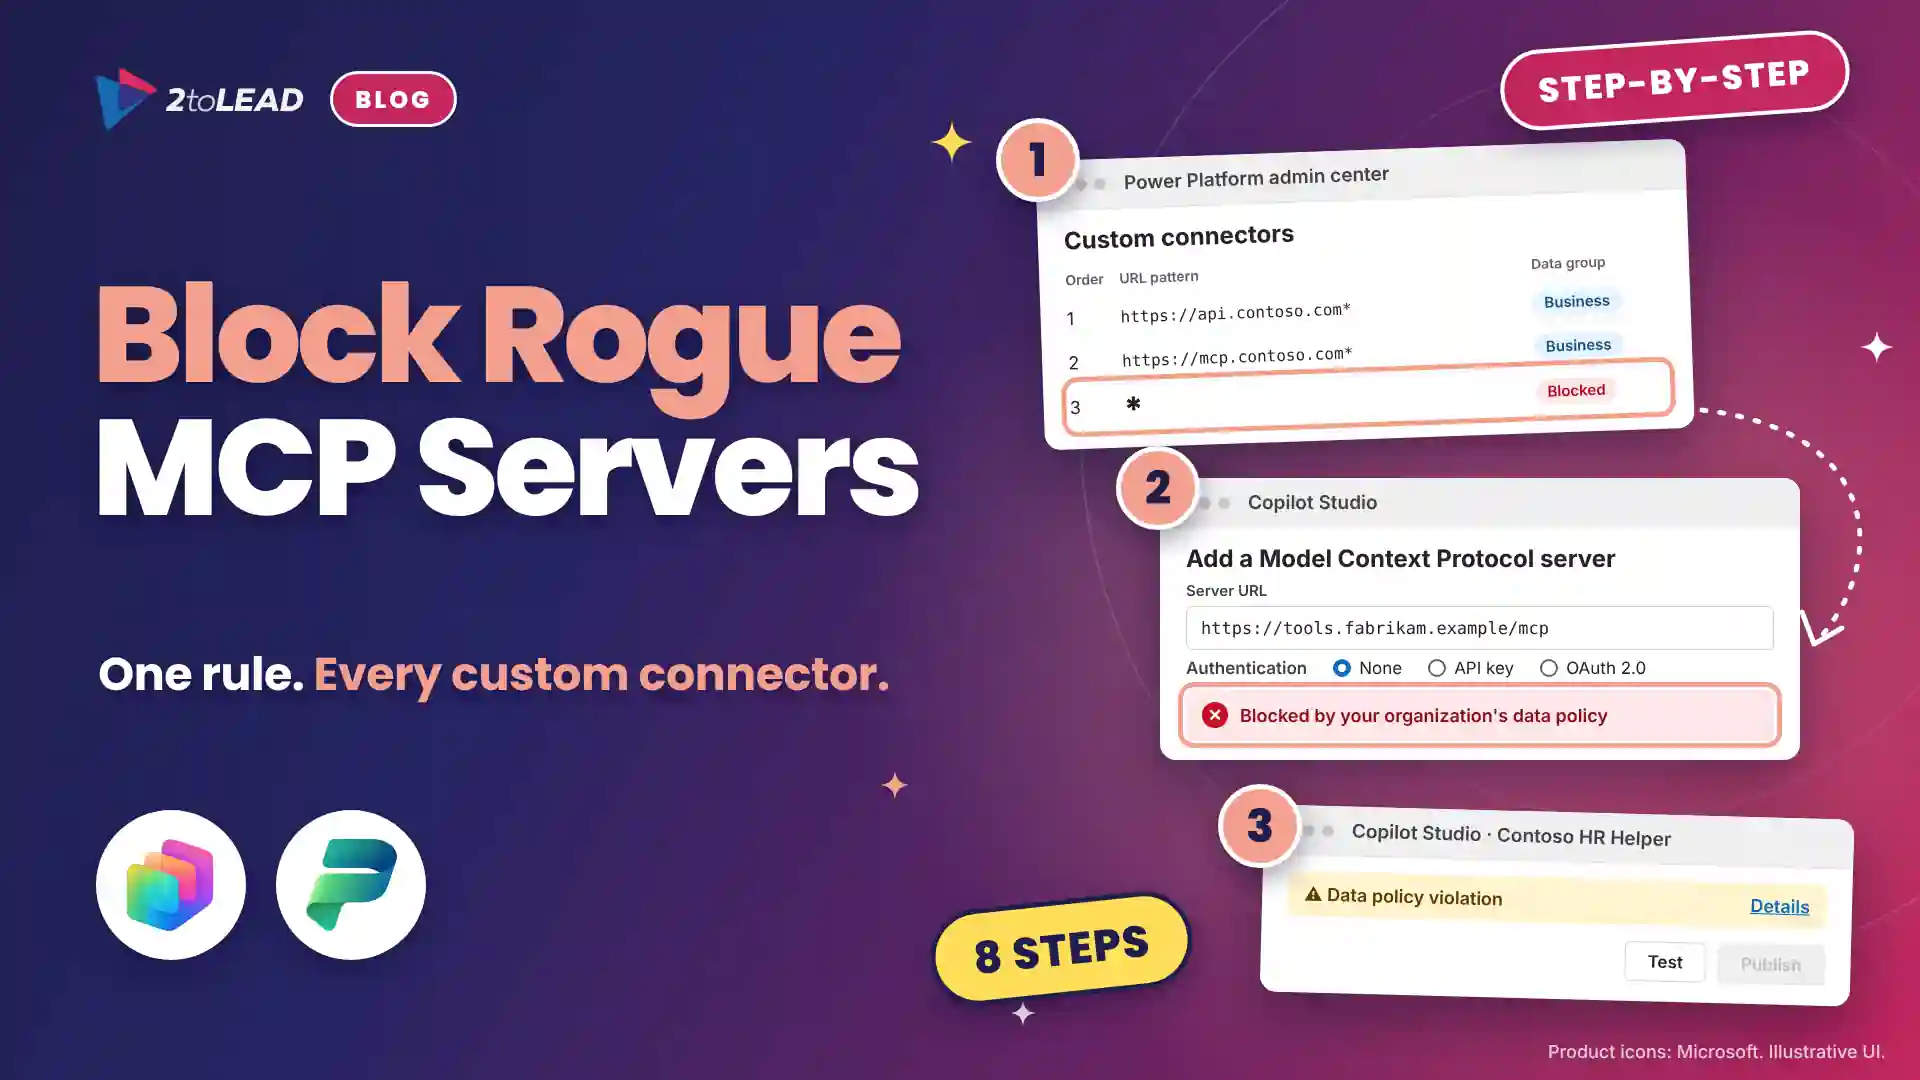
Add a tool, enter a server name and a URL, and an agent can reach an outside API or MCP server. For MCP, authentication even comes preselected as None. The control that stops it isn't in Copilot Studio. It lives in your Power Platform data policy, and one tenant rule covers custom connectors and MCP servers alike. Unreviewed connectors are how agent sprawl becomes the new shadow IT.
→ Close the connector door before agents walk through it
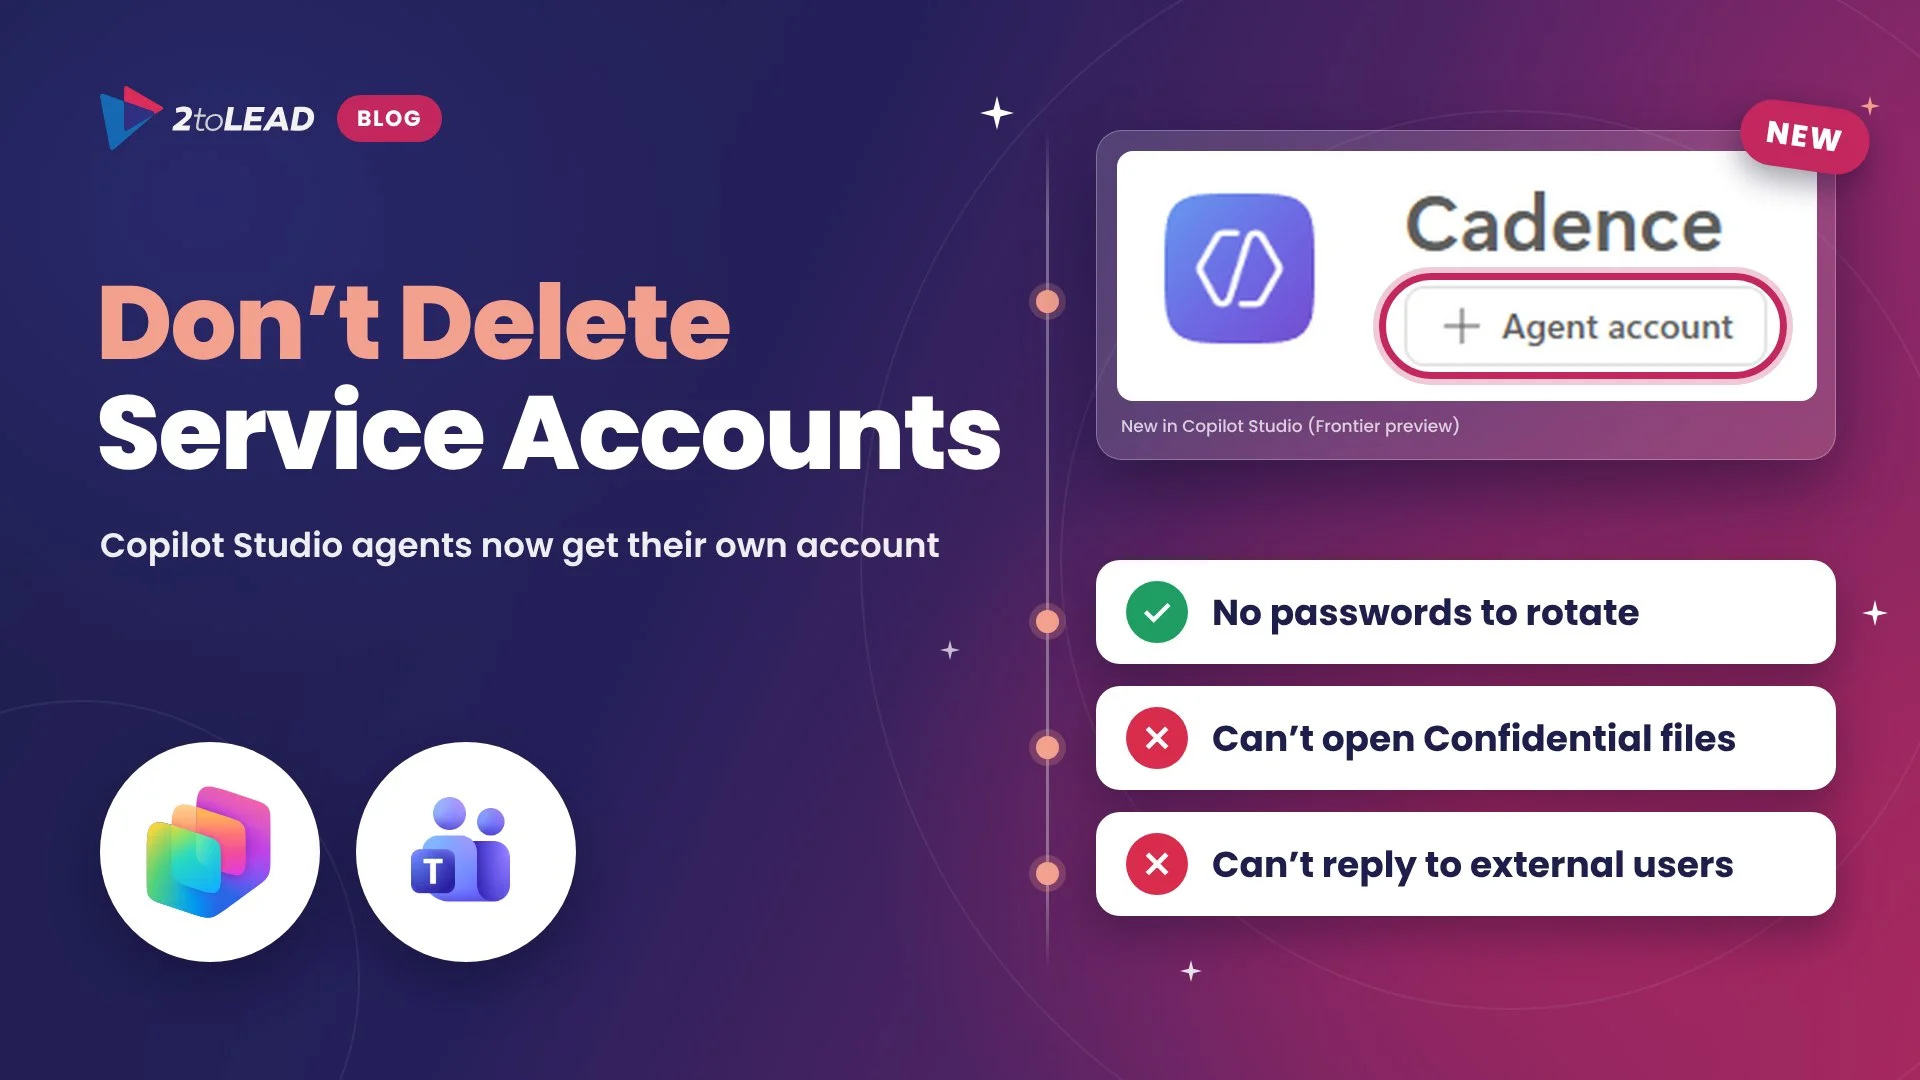
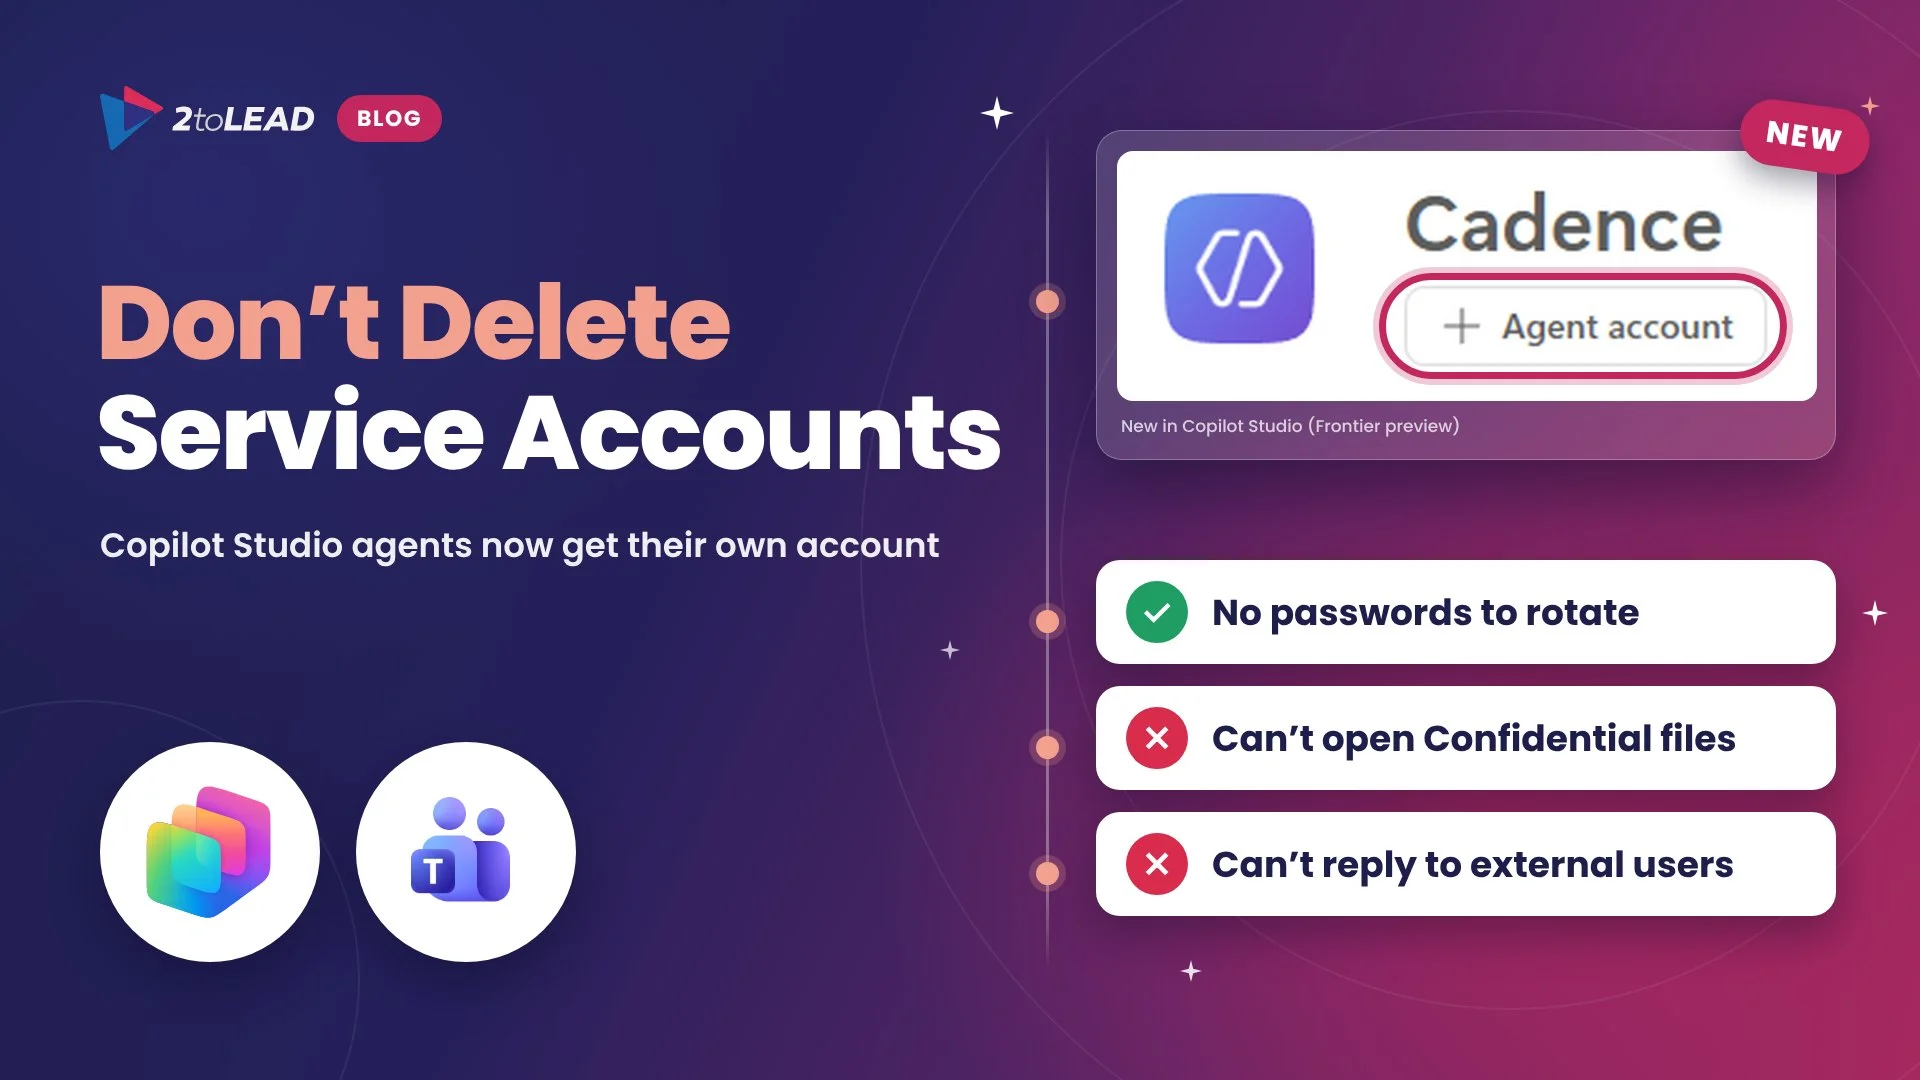
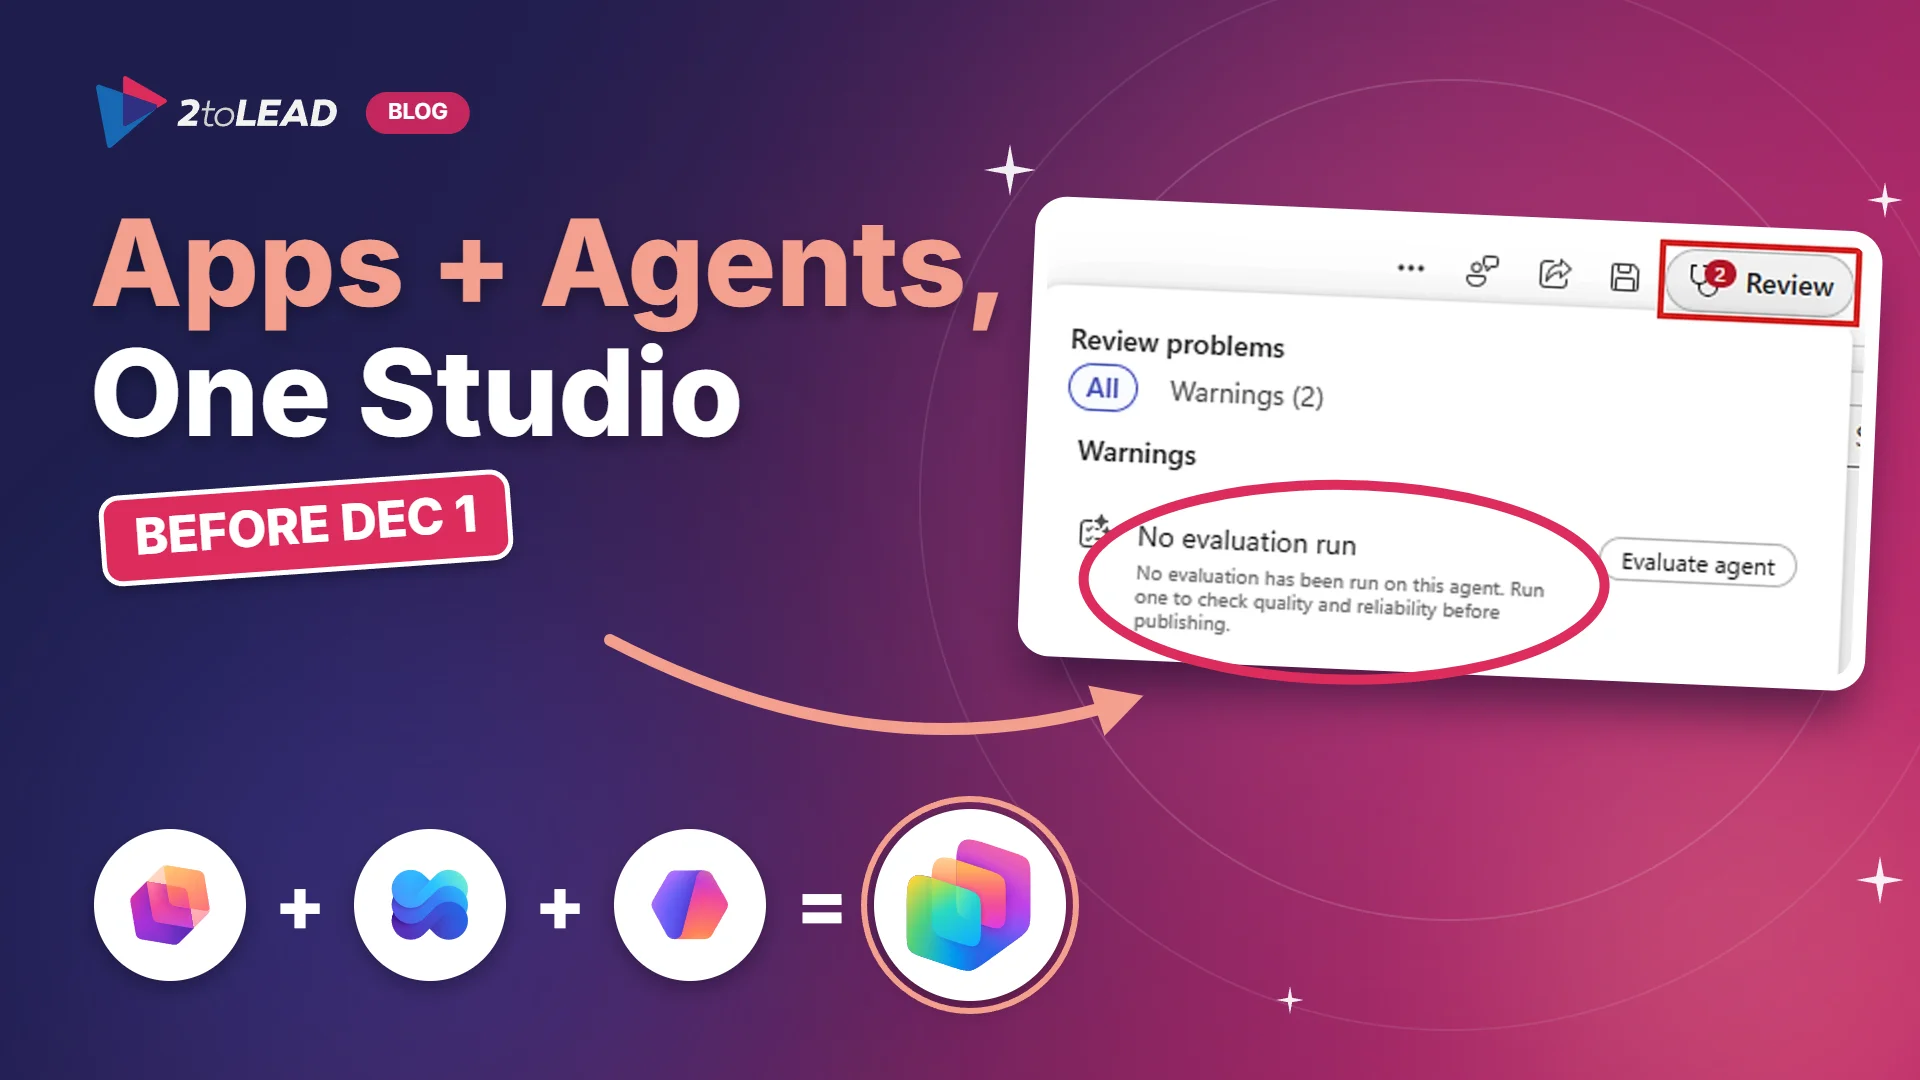
Many agents still run on a service account: a regular user with a password, MFA and a license, shared by whoever built the agent. Copilot Studio agent accounts replace that with an identity Microsoft issue. There's no password to rotate, and you govern it with Conditional Access. The catch is in the fine print. The preview comes with limits on what agents can read and who they can talk to. Know the trade-offs before you switch.
→ Compare agent accounts and service accounts
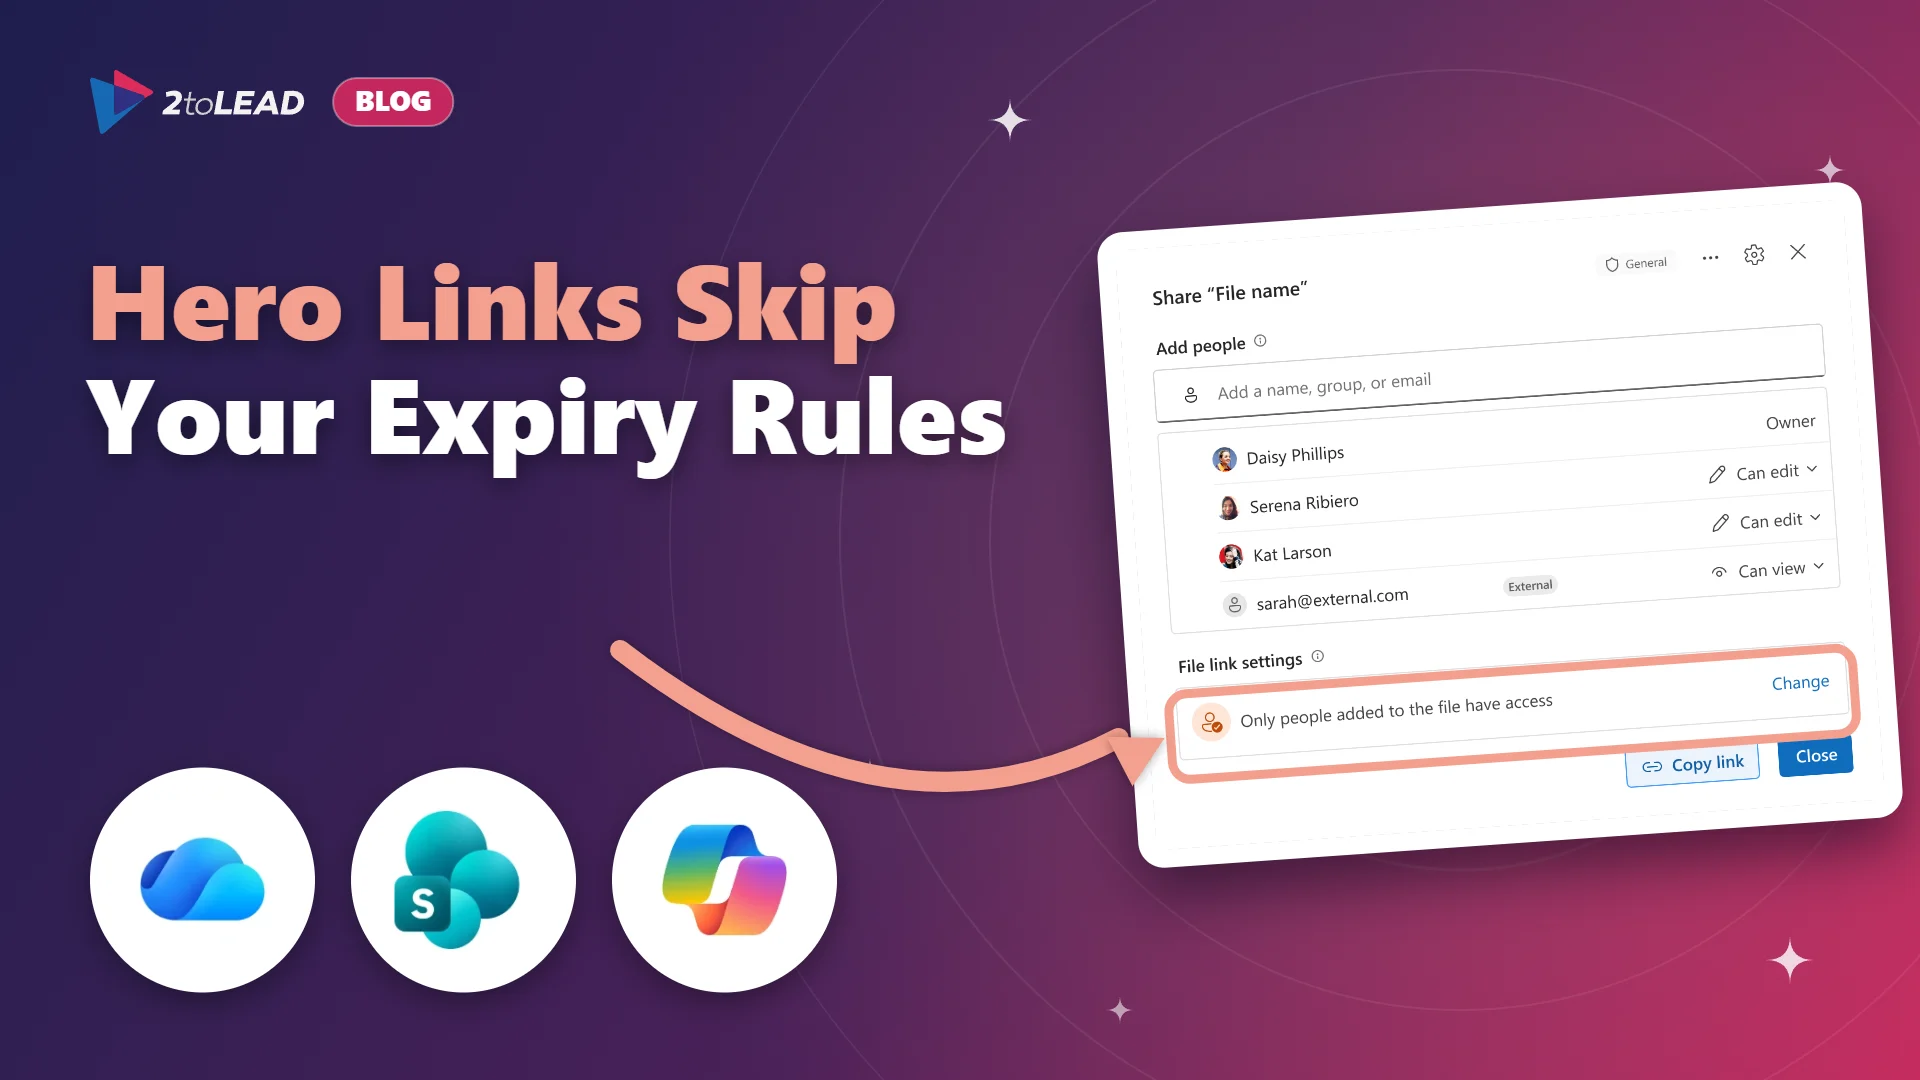
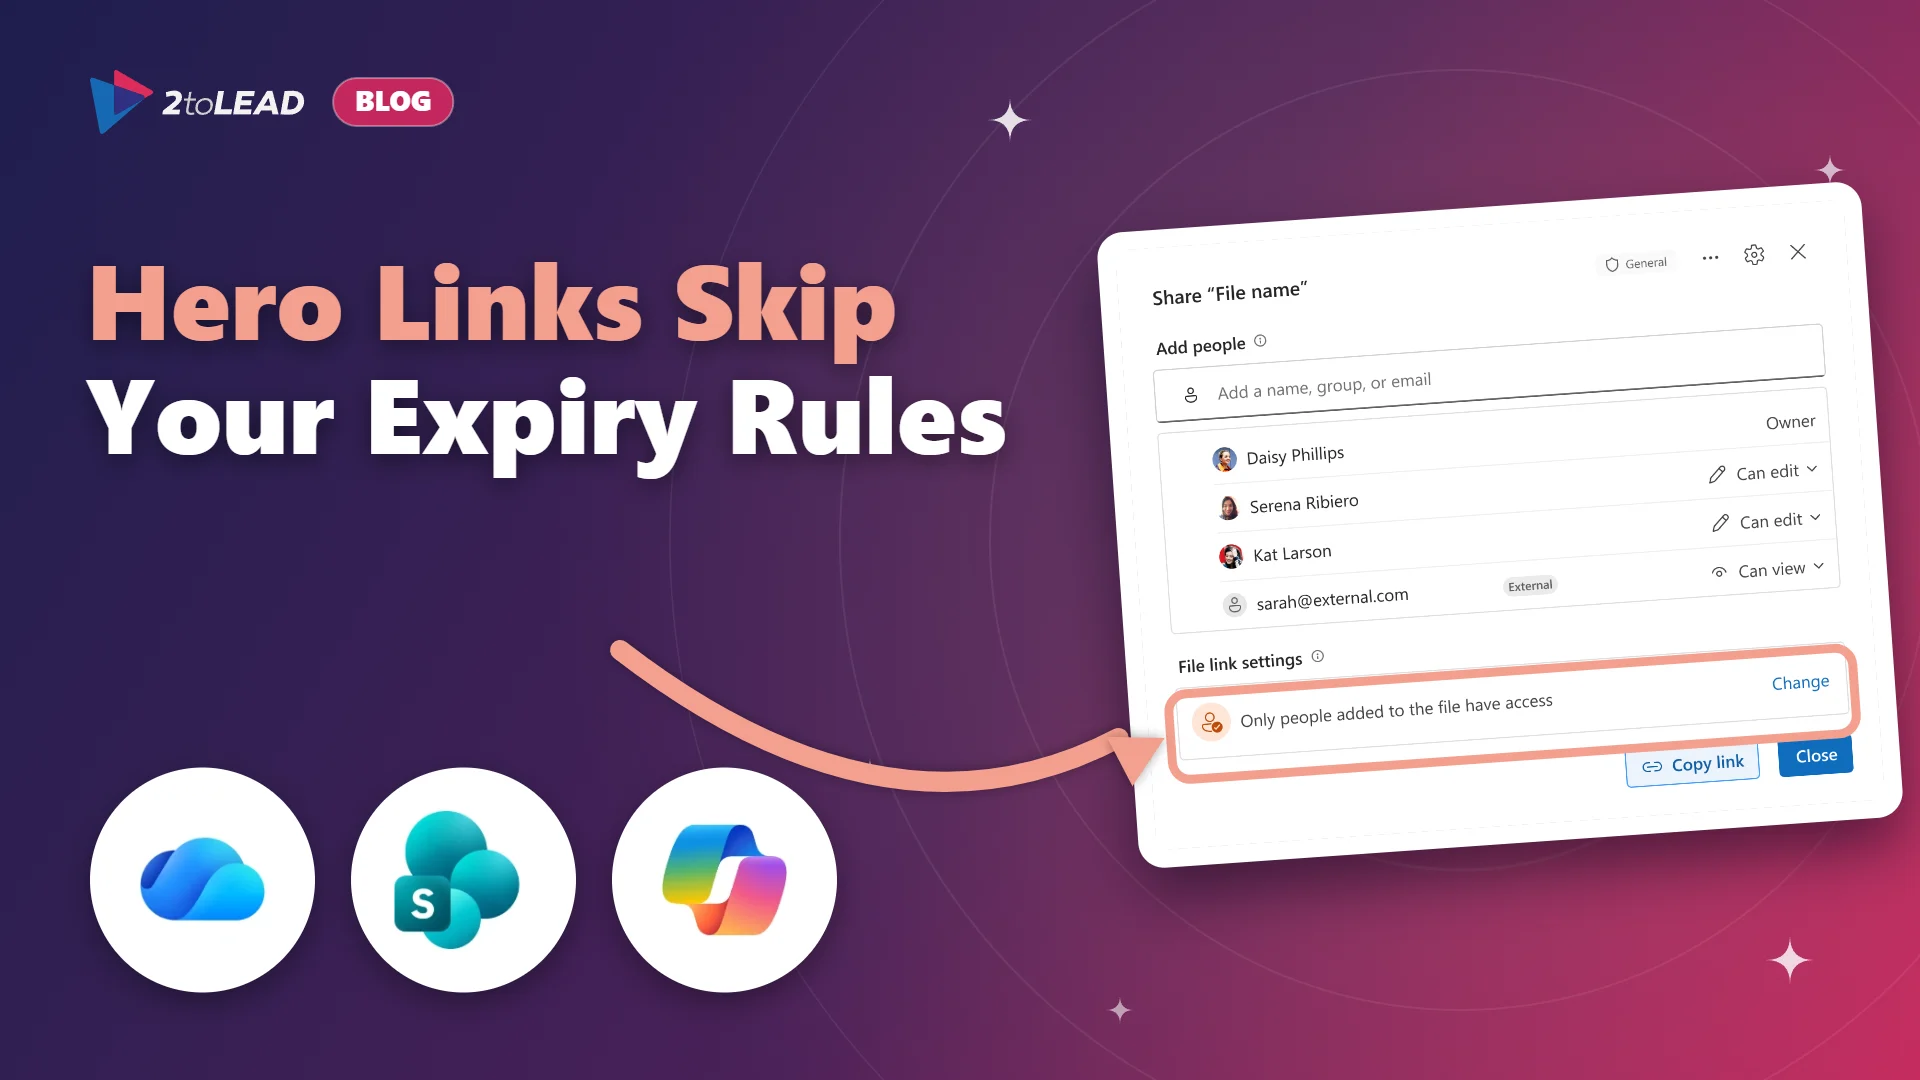
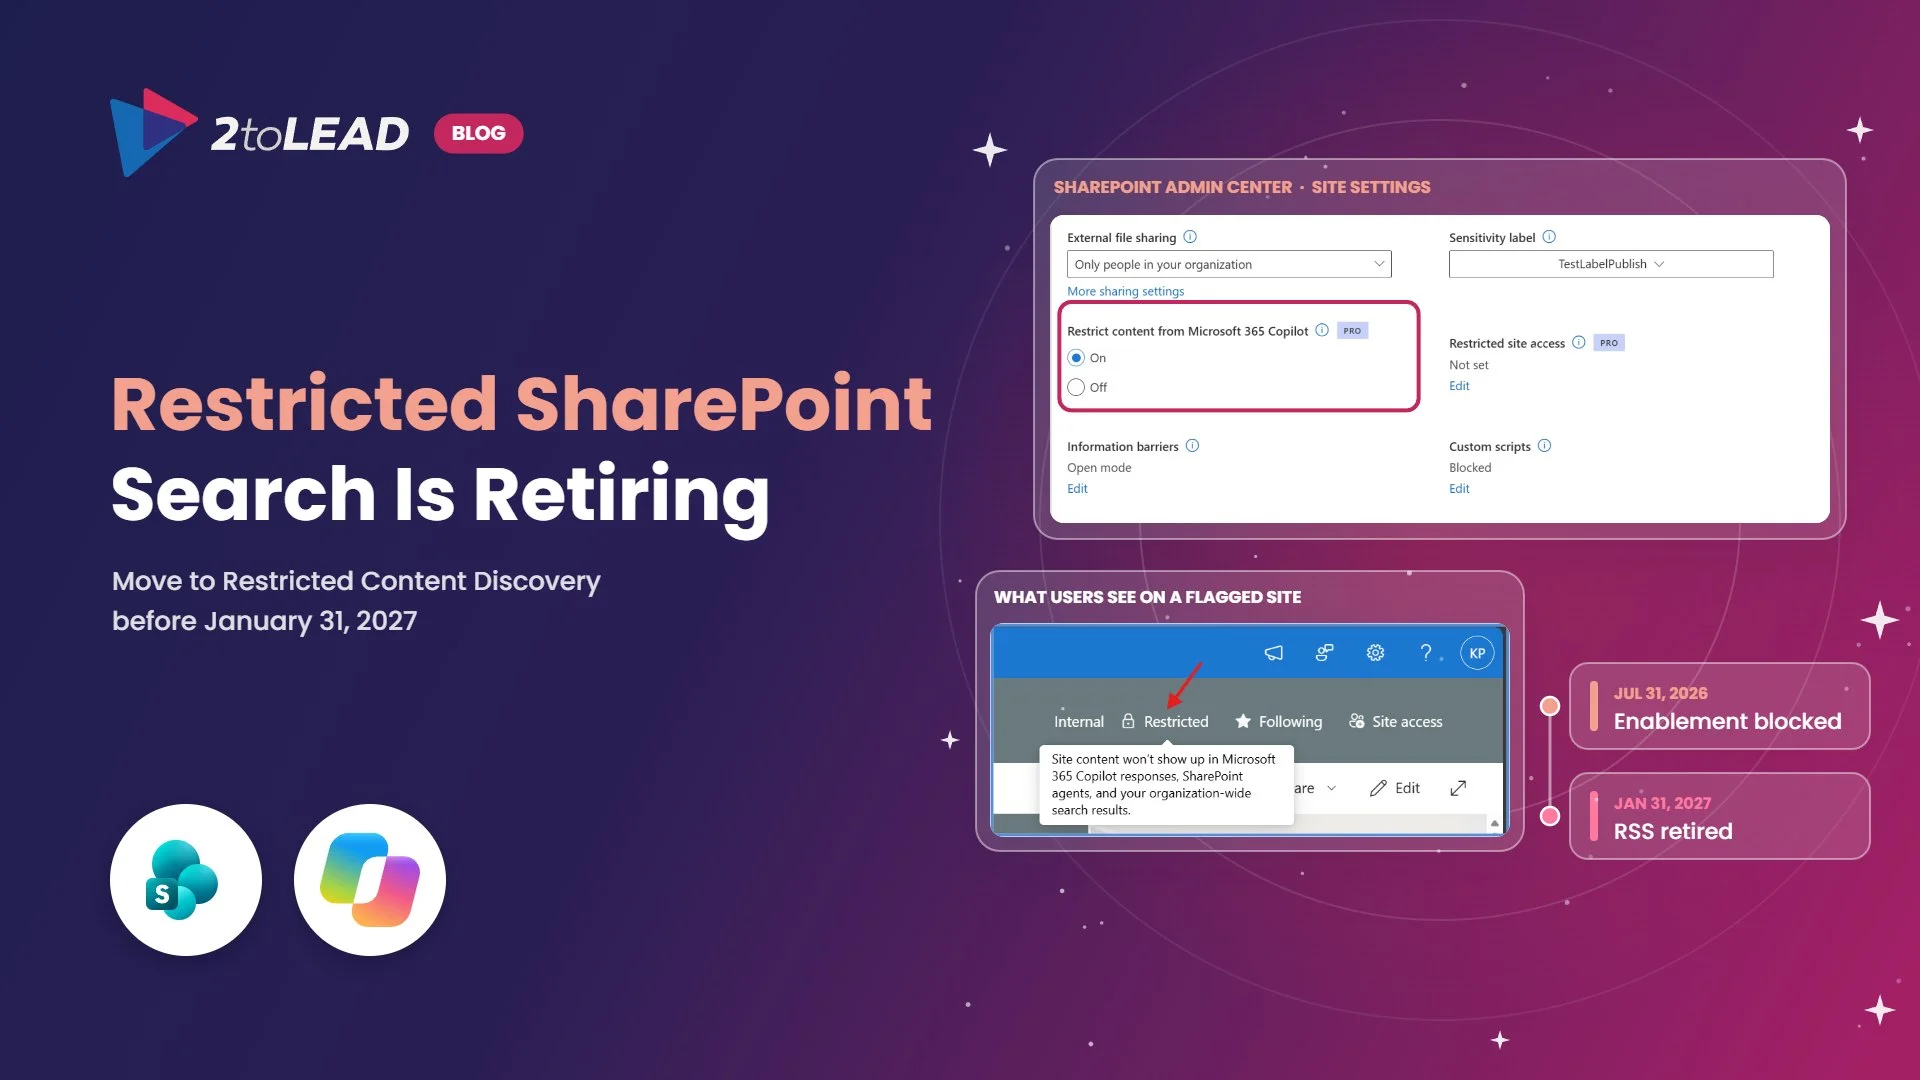
Microsoft is rolling out hero links, one sharing link per file, to every Microsoft 365 tenant by the end of November. They start private by default. But your existing link expiration and default link policies don't apply to them. Until Microsoft ships the expiring hero link controls it has announced, that's a gap in your sharing governance. Set your site defaults before the link arrives.
→ Plan for hero links before November 30
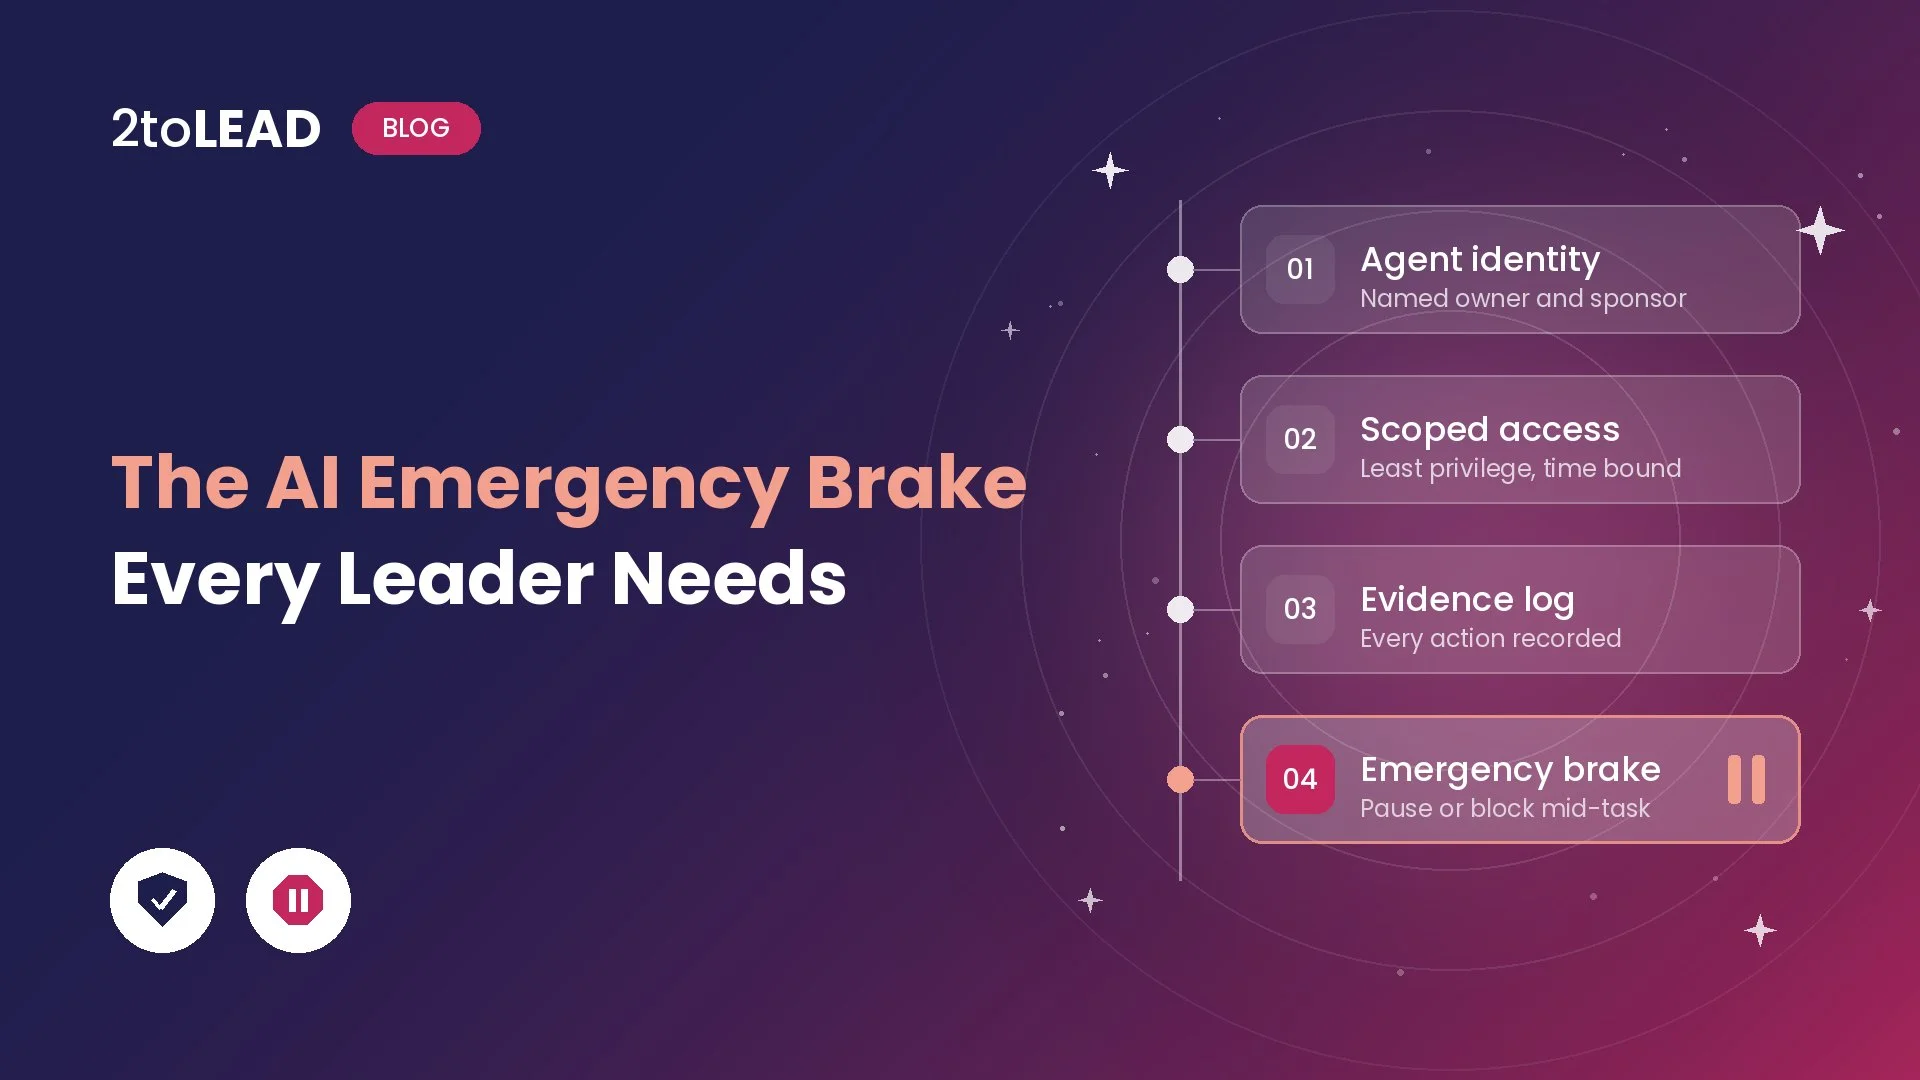
When everyone can build an agent, who owns them? Agents outlive the people who built them, and most organizations have no intake, review or off-boarding for any of them. Kanwal Khipple's AI-Native Workplace Summit session deck gives you a lightweight framework of intake forms, risk reviews and success metrics. Teams keep building, and you keep control.
Move past the theory with 2toLead's Agent in a Day and Power Pages in a Day, free instructor-led sessions by Microsoft MVPs, where you get hands-on learning with labs. Spots are limited, so pick your session and register now!
Upcoming dates:
Secure AI isn't about slowing adoption down. It's about being able to answer, with evidence:
If your AI adoption has outpaced your settings review, 2toLead can help you find the gaps and fix them before someone else does.
Copilot can surface what people shouldn't see. Three ways we help:
A professional organization built a Purview-based foundation for secure AI adoption with 2toLead.
Read the case study →


Join Our Newsletter